



Security Audits, Checks & Inspections: A Complete Management Guide
A practical guide to running audits, checks and inspections that hold up under scrutiny, from setting the standard to closing out every finding.
Most compliance failures are not caused by missing policy. They are caused by inconsistent execution.
A fire door check gets skipped on a busy shift. An audit finding gets written up, then filed away and forgotten. A contractor signs off an inspection that nobody ever reviews. None of these are dramatic failures on their own. Together, they are how organisations end up unable to answer a simple question after an incident: can you prove this was checked?
For security and facilities teams managing commercial buildings, retail estates, or large portfolios, audits, checks and inspections are the evidence base for everything else. They demonstrate that fire safety systems work, that access control is enforced, that contractors are doing what they are paid to do, and that the organisation is meeting its legal duties, from the Building Safety Act 2022 to Martyn’s Law.
This guide covers what audits, checks, inspections and assessments actually are, why they matter for compliance, how to build a programme that produces defensible evidence, how that looks slightly differently depending on your sector, and what changes when you move the whole process off paper.
Audits, checks and inspections: three different jobs
These terms get used interchangeably, which causes real problems. A programme that treats a daily fire door check the same way as an annual ISO 22301 audit will either over-engineer the simple work or under-evidence the serious work.
Each activity has a different purpose, a different frequency, and a different audience.
| Activity | Purpose | Typical frequency | Who it’s for |
|---|---|---|---|
| Check | Routine verification that a control is in place and working | Daily or per shift | Site teams, supervisors |
| Inspection | Deeper look at a specific system or asset to catch problems early | Weekly to quarterly, risk-based | FM teams, engineers, contractors |
| Audit | Formal evaluation against a defined standard or framework | Quarterly to annually | Compliance teams, insurers, regulators |
| Assessment | Evaluation of readiness or risk, with severity ratings attached | Ad hoc or annual | Security, compliance, and risk leads |
A useful way to think about it: checks catch the everyday, inspections catch the technical, audits catch the systemic, and assessments catch the strategic. A mature programme runs all four, at the right cadence, and links them so a failed check can trigger an inspection, and a pattern of failed inspections can trigger an audit.
Why audits, checks and inspections matter for compliance
Audits, checks and inspections are not paperwork for its own sake. They are the mechanism that lets an organisation prove, after the fact, that it did what it said it would do. In commercial real estate and facilities management, that proof is increasingly a legal requirement, not just good practice.
The Building Safety Act 2022 and the golden thread
For higher-risk buildings, the Building Safety Act 2022 introduced the concept of a golden thread: a continuous, accessible digital record of information about a building, from design through to occupation. Audits, checks and inspections are a core part of that thread. If the Building Safety Regulator asks for evidence that fire safety systems have been maintained and checked, a spreadsheet on someone’s laptop is not going to satisfy the request.
RIDDOR and incident-linked evidence
Where a check or inspection failure contributes to a reportable injury or dangerous occurrence, RIDDOR record-keeping duties apply. Having a documented history of checks and inspections, including what was found and what was done about it, is what turns a defensible position into an indefensible one, or vice versa.
Insurance and contractor accountability
Insurers increasingly expect evidence that scheduled maintenance and safety checks actually happened, not just that a policy exists saying they should. In multi-tenant CRE assets, audits and checks are also how landlords and occupiers evidence who was responsible for what on demised premises, which matters when something goes wrong and liability is being apportioned.
| Martyn’s Law: where audits and checks fit inMartyn’s Law (the Terrorism (Protection of Premises) Act 2025) introduces duties for organisations responsible for publicly accessible premises to assess risk and put in place, and evidence, appropriate procedures.Audits, checks and inspections are the record-keeping layer that supports this: they show that procedures are not just written down but actually being carried out.The SIA’s Section 12 operational guidance remains in draft and consultative form at the time of writing, so organisations should treat specific guidance details as subject to change rather than settled requirements. |
How to run a security audit that stands up to scrutiny
An audit is only useful if it produces evidence someone else can rely on: an insurer, a regulator, a client, or your own board. That means the process matters as much as the checklist. Here is a structure that holds up.
1. Define the scope and the standard
Decide what you are auditing against before you decide what to look at. This might be an ISO standard, an insurer’s requirements, a client’s contractual specification, or an internal policy built around a specific legal duty. Vague scope produces vague findings, and vague findings are the ones that get argued with rather than acted on.
2. Build or select the right template
A generic checklist applied to every site misses site-specific risk. A tall building with public access has a different risk profile to a low-footfall warehouse. Templates should reflect the site’s actual risk profile, not a one-size-fits-all standard, and should be built or adapted by someone who understands that site, not copied wholesale from a library.
3. Schedule by risk, not by convenience
Higher-risk sites and systems should be audited more often. Fixed annual cycles applied uniformly across a portfolio tend to under-audit the sites that need it most and over-audit the ones that do not. A simple risk tier, high, medium, low, mapped against audit frequency gives most portfolios a defensible scheduling logic without over-engineering it.
4. Capture evidence, not impressions
Photos, timestamps, and notes tied to specific findings turn an audit from an opinion into evidence. Where a finding is a non-conformity, record the severity and the reason, not just a pass or fail, so whoever picks up the finding later understands why it matters without needing to ask the auditor directly.
5. Score and prioritise findings
Not every finding carries the same risk. A missing fire extinguisher sign and an unsecured fire exit are not the same problem. Severity thresholds let teams triage what needs fixing today against what can wait, and stop urgent issues from getting lost in a long list of minor ones.
6. Turn findings into tracked actions
An audit finding with no follow-up is a liability, not a safeguard. Every non-conformity should become a task with an owner and a deadline, ideally linked automatically rather than transcribed by hand into a second system, where details get lost or simply never make the transfer.
7. Close out and retain the record
An audit is not complete when the report is issued. It is complete when every finding is closed out and the full record, findings and resolution, is retained centrally for the next audit, the next insurance renewal, or the next regulator request. Retention matters as much as capture: a record nobody can find six months later has little practical value.
8. Review the template itself
Audit templates go stale. Review them periodically against new risks, new regulation, and lessons learned from findings and incidents, so the audit keeps testing the things that actually matter rather than the things that mattered when the template was first written.
Scheduling audits, checks and inspections by risk tier
Frequency is where most programmes either overspend effort or leave gaps. A simple risk-tiered approach, applied consistently across a portfolio, tends to work better than either a fixed calendar or an ad hoc schedule driven by whoever raises a concern loudest.
| Risk tier | Example site or system characteristics | Suggested audit frequency | Suggested check frequency |
|---|---|---|---|
| High | Publicly accessible venues, life safety systems, high footfall CRE assets | Quarterly | Daily |
| Medium | Standard commercial offices, moderate footfall, non-critical plant | Twice yearly | Weekly |
| Low | Low-footfall storage, non-critical fixtures, back-of-house areas | Annually | Monthly |
These bands are a starting point, not a fixed rule. The right tier for a given site or system should be set by an actual risk assessment, informed by footfall, criticality, and any relevant legal duty, rather than assumed from a building’s size or age alone.
Building a facility inspection programme
Inspections sit between checks and audits: more technical than a daily walkthrough, more frequent than a formal audit. They are where problems in plant rooms, fire safety systems, and building services get caught before they become incidents.
A well-structured facility inspection programme typically covers:
- Life safety systems: fire alarms, sprinklers, emergency lighting, fire doors.
- Plant and mechanical systems: HVAC, lifts, generators, water systems.
- Building fabric: structural elements, roofing, external areas.
- Building management systems (BMS): where inspections verify that automated monitoring is functioning as intended, not just trusted blindly.
Frequency should be tiered by criticality. A life safety system with a direct line to occupant safety warrants a tighter inspection cycle than a decorative fixture. Where an inspection requires specialist knowledge, contractor sign-off and e-signatures give the record the same weight as an in-house inspection.
The value of inspections is almost entirely in how early they catch problems. A plant room fault found on a routine inspection is a maintenance job. The same fault found because a system has already failed is an incident, a disruption, and often a much larger bill.
What belongs on a security audit checklist
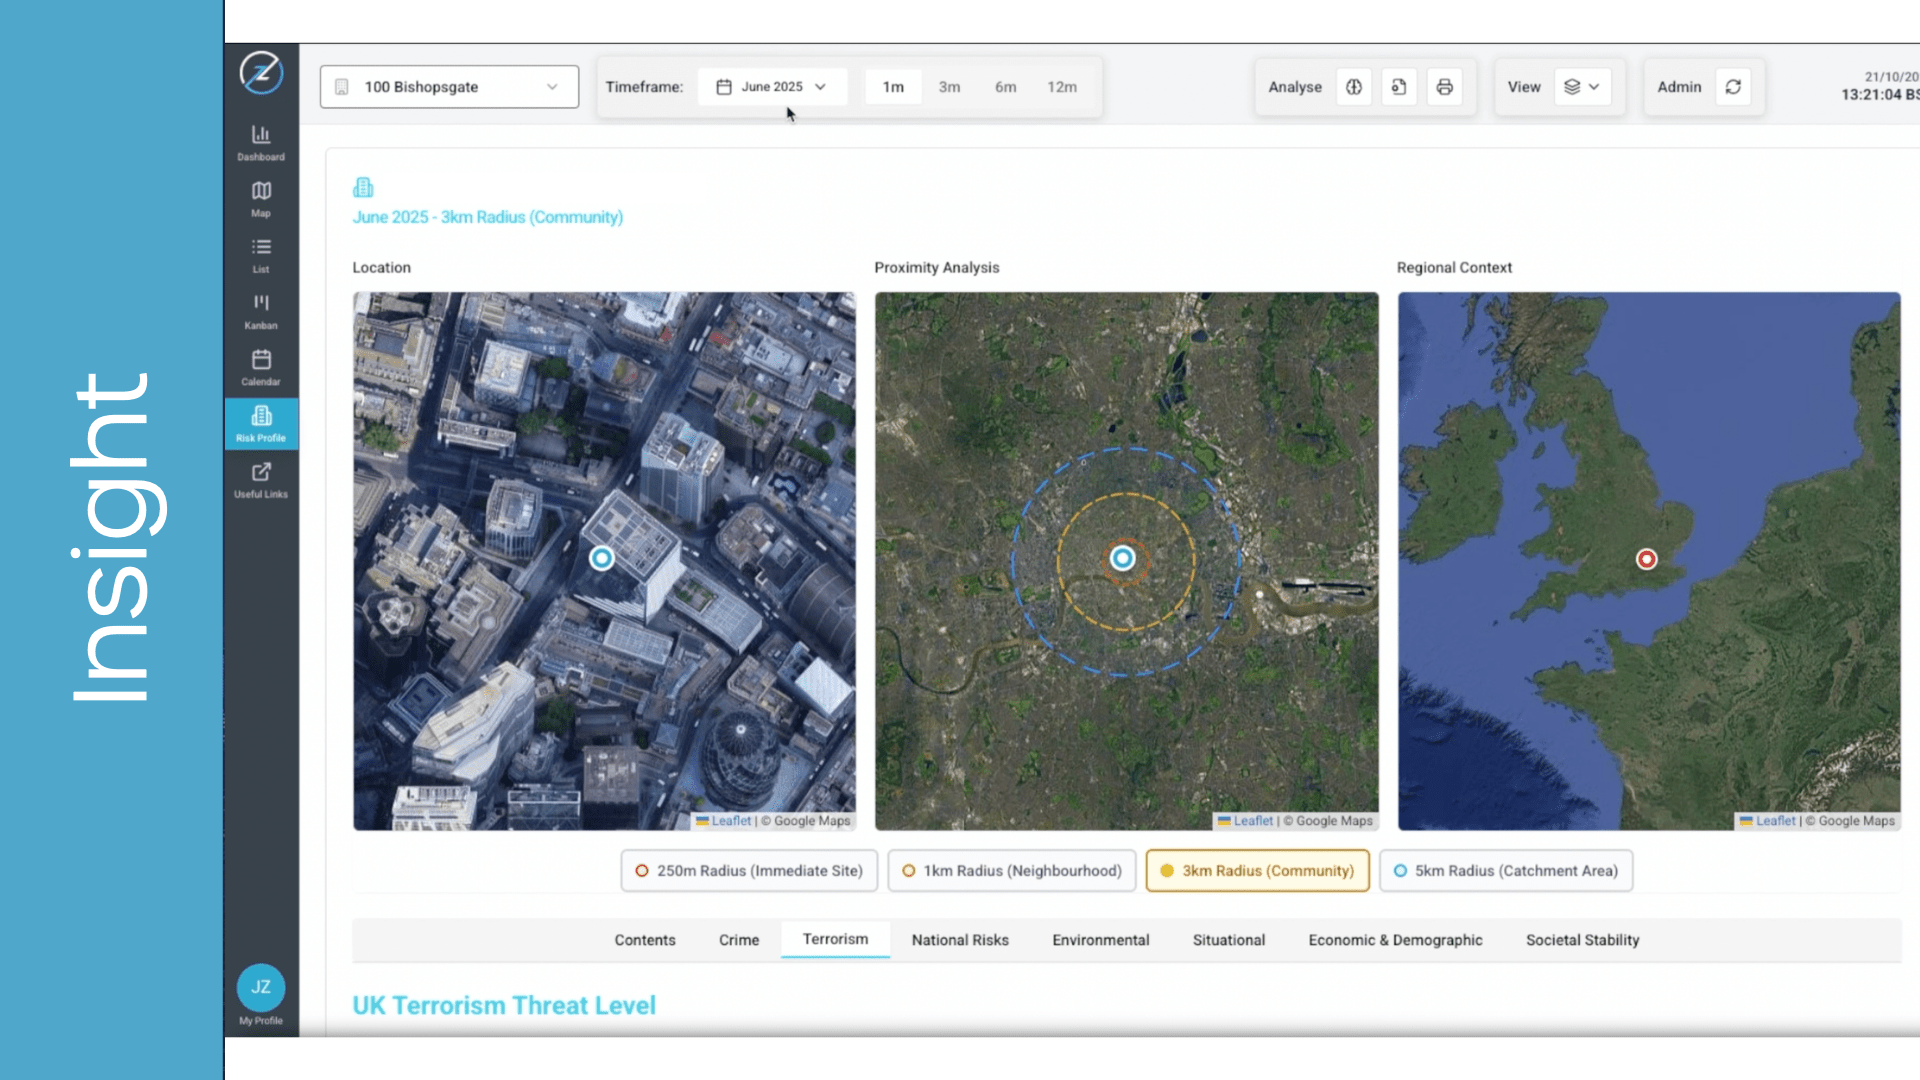
A checklist is only as good as its coverage. Too narrow, and it misses real risk. Too generic, and it becomes a box-ticking exercise that nobody takes seriously. The categories below are a starting point, not a template to copy exactly, because the right checklist reflects the specific risks of the site it covers, in the same way a Location Risk Profile is built around what actually threatens a given building rather than a generic risk list.
| Category | Example items | Typically owned by |
|---|---|---|
| Physical security controls | Access control function, CCTV coverage gaps, lock and key integrity | Security team |
| Life safety compliance | Fire doors, alarm tests, extinguisher checks, emergency lighting | FM / security team |
| Procedural evidence | SOP and EOP records, training completion, drill logs | Compliance / operations lead |
| Documentation | Risk assessments, insurance certificates, contractor accreditation | Compliance manager |
| Site-specific risk items | Items flagged by the site’s own risk profile or recent incidents | Security / risk lead |
Two categories are worth calling out. Procedural evidence, showing that standard operating procedures and emergency operating procedures are actually being followed, is often the weakest part of an audit trail, because it depends on records that live outside the audit itself. And site-specific risk items are what stop a checklist from being generic: a checklist built from a site’s actual threat and risk profile will always outperform one copied from a template library.
How this looks different by sector
The core discipline of audits, checks and inspections is consistent everywhere. What varies is the emphasis, driven by who owns the risk and who is asking for evidence.
Security and FM service providers
Providers managing multiple client sites need a programme that is consistent enough to prove standards across contracts, but flexible enough to reflect each client’s specific requirements. Client-facing reporting matters here almost as much as the audit itself: a provider that can produce a clean, structured audit trail on request has a real commercial advantage when contracts are up for renewal.
Commercial real estate portfolio and facilities teams
CRE teams are usually managing the split between landlord and occupier responsibility on demised premises, alongside portfolio-wide oversight. The priority is often less about any single site’s checklist and more about being able to see compliance status across an entire portfolio at a glance, so gaps are visible before an insurer, tenant, or regulator finds them first.
Retail loss prevention teams
For retail estates, checks and inspections often sit alongside loss prevention activity, covering access points, stockroom security, and till area controls, as well as the standard fire and life safety items. Frequency tends to be higher given footfall and stock risk, and findings often need to escalate into case management rather than a routine task, particularly where theft or deliberate damage is suspected.
Roles and responsibilities across the audit lifecycle
Audits, checks and inspections fail when responsibility is unclear. Different roles own different parts of the lifecycle, and the handoffs between them are where records get lost.
| Role | Typical activity | Frequency |
|---|---|---|
| Security officers | Daily and shift-based checks, often completed during patrols | Daily / per shift |
| FM teams and contractors | Technical inspections of plant, systems, and building fabric | Weekly to quarterly |
| Compliance or H&S managers | Formal audits, non-conformity tracking, close-out oversight | Quarterly to annually |
| Senior leadership / accountable person | Assurance reporting, golden thread oversight, board reporting | Ongoing / periodic review |
Under the Building Safety Act 2022, the accountable person duty makes this chain of responsibility explicit for higher-risk buildings: someone at a senior level is answerable for whether the evidence exists, not just whether the work was technically done. That makes clean handoffs between roles a compliance requirement, not just good practice.
Common pitfalls that undermine compliance
Paper records that get lost, damaged, or simply never make it back to a central file. A single missing form is rarely the problem on its own, until it is the exact form a regulator asks for.
Generic checklists reused across sites with very different risk profiles. A template built for one building rarely fits another, and the gaps only show up when something has already gone wrong.
Findings that get recorded but never escalated, so nothing actually closes out. A logged issue with no owner and no deadline is functionally the same as no record at all.
No portfolio-wide visibility, with each site running its own version of the process in a local spreadsheet. Compliance gaps at one site are invisible to the rest of the organisation until an audit or incident forces the comparison.
Over-reliance on infrequent formal audits, without the daily checks that catch problems while they are still small. By the time an annual audit finds a fault, it may have been live for months.
Most of these are not caused by lack of effort. They are caused by a process that depends on manual transcription between systems, at every one of which information can be lost, delayed, or quietly dropped.
Moving from paper to digital: what changes
Digitising audits, checks and inspections is not simply about replacing a clipboard with a tablet. It changes what the record can actually do.
- Evidence is captured in the moment, with photos, notes, and timestamps attached directly to the finding, rather than written up later from memory.
- Offline capture means checks and inspections can be completed in basements, plant rooms, or remote sites without signal, syncing automatically once reconnected.
- Failed items escalate automatically into a task or an incident, instead of waiting for someone to notice a paper form later.
- Every result feeds a single, searchable record, rather than sitting in a filing cabinet or an isolated spreadsheet at one site.
The result is a record that can actually answer the question a regulator, insurer, or board member is likely to ask: not just ‘was this checked’, but ‘show me’.
How Zinc connects audits, checks and inspections to your wider operation
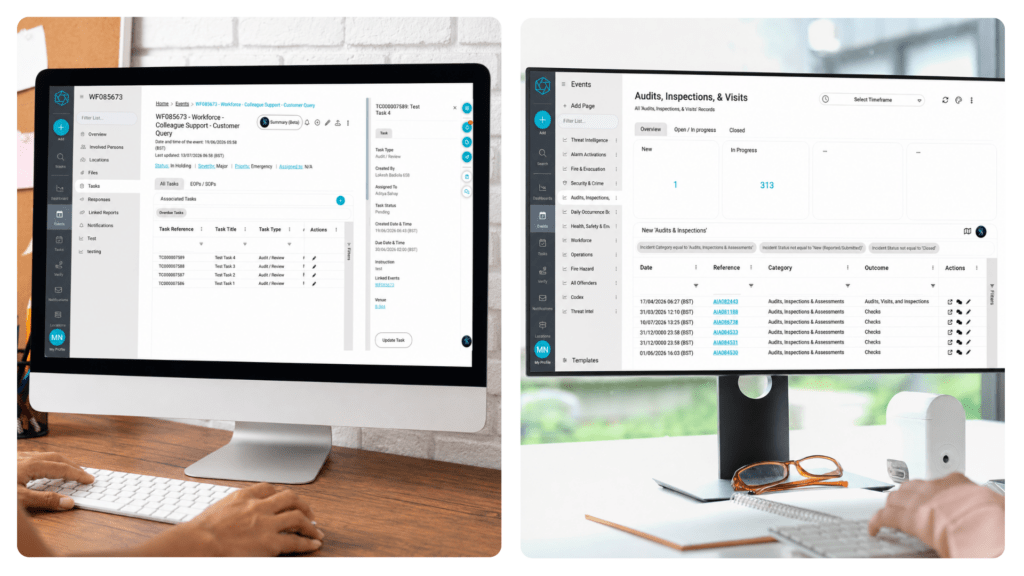
Audits, checks and inspections do not happen in isolation, and treating them as a standalone system is one of the most common reasons evidence ends up fragmented. Zinc’s Audits, Checks & Inspections module is built to connect directly into the rest of the platform, rather than sitting alongside it as a separate tool.
- Over 50 ready-to-go compliance templates, covering health and safety, security, ISO, and facilities activities, alongside the ability to build custom templates for site-specific risk.
- Failed checks and critical findings escalate straight into Incident Management, so nothing urgent waits for someone to notice it on a report.
- Every follow-up action becomes a task through Tasks & Procedures, assigned and tracked to close-out rather than left as an open item nobody owns.
- Officers can complete checks and inspections as part of their Patrol Management routes, so routine compliance activity happens alongside existing operational work rather than as a separate exercise that competes for time.
- Every result feeds Data Analysis & Reporting, giving one live view of compliance status across an entire portfolio rather than site-by-site.
Capture itself is designed for the field, not the office. Dynamic forms guide accurate data entry, voice-to-text speeds up note-taking on the move, and offline access means checks and inspections can be completed in basements, plant rooms, or remote sites without signal, syncing automatically once the device reconnects. Evidence, photos, annotated notes, signatures, and contractor sign-offs, is attached at the point of capture, not reconstructed later from memory.
Organisations using Zinc’s platform to standardise this process have reported meaningful gains: improved audit pass rates from consistent, escalation-backed checklists, fewer contractor call-outs because issues are caught and resolved in-house before they escalate, and measurably faster hazard identification through mobile inspections that surface issues before they turn into costly failures.
For organisations working towards Martyn’s Law readiness, this connected structure also matters. The law’s requirement for documented, evidenced procedures is easier to meet when checks, inspections, and their resolution already live in one auditable record, rather than being assembled after the fact from several disconnected sources.
For more information on becoming Martyn’s Law ready, read our article Understanding Martyn’s Law: What It Means for UK Businesses
Building an audit programme that holds up
Audits, checks, inspections and assessments are not four names for the same thing. They are four different disciplines, each with its own purpose, frequency, and audience, and a mature compliance programme runs all of them, deliberately linked together.
The organisations that get this right are not the ones running the most audits. They are the ones whose checks catch problems early, whose findings turn into tracked actions, and whose records can answer a hard question the moment it is asked, whether that question comes from a regulator, an insurer, or a board.
If your current programme cannot produce that evidence quickly, the gap is rarely effort. It is usually the process connecting the pieces.
Explore Zinc’s Audits, Checks & Inspections module and discover how automated process could help your business.


 +44 (0)20 3989 4859
 info@zinc.systems

